Overview #
Ever thought about when a user opens a file from a zip using any zip tool, how zip tool opens file, and whether it stores this file anywhere on disk or creates any forensic evidence for DFIR analysts? Does there is any forensic evidence that can help to prove that a file was opened, and is it possible to identify which zip tool is used to open the zip file? I was also thinking, one day while opening a zip file, what information can be found on disk for the zip activity, and this blog is the result of research I did to answer my questions of forensic artifacts created by zip tools.
If you spot any mistakes or areas for improvement in my blog, feel free to reach out to me via email or on any platform. I welcome constructive feedback and am always eager to enhance the quality of my content.
Disclaimer: All information shared on this blog is strictly for educational and research purposes. Use tools and techniques only on systems you own or have explicit permission to test. The author is not responsible for any misuse of the information.
What is the Goal of Research? #
Let’s understand what the goal of research is, what evidence will be checked, or what zip tool evidence will try to find. In this research, the purpose is to find whether analysts can determine if any file is opened using any zip tool or not. If a file is opened from a zip tool, how to prove that access activity? Finally, can analysts also get the file opened from a zip even if the zip file is deleted from the device/system? This research only focused on Windows operating system.
Zip Tools Observations #
There are two locations where zip tool observations are recorded and analysed: first is from the system disk and second is from an external USB. The reason for two locations is to understand if both locations generate the same or different evidence.
This research covers 5 zip tools:
| Tool | Version |
|---|---|
| 7z | 26.02 (x64) |
| Windows Explorer | N/A |
| Winrar | 7.23 (64-bit) |
| PeaZip | 11.2.0 - win64 build, x86_64 |
| NanaZip | 6.5.1767 (x64) |
Zip File On System #
On the system, all temporary files are created by tools in the location C:\Users\<username>\AppData\Local\Temp.
| Tool | Delete Files on Next Run | Can Run Executable | Can Load All Files in Temporary Location | ||
|---|---|---|---|---|---|
| 7z | ❌ | 💠With Dependencies: ❌ 💠Without Dependencies: ✅ |
❌ | ||
| Windows Explorer | ❌ | 💠With Dependencies ❌ 💠Without Dependencies: ✅ |
❌ | ||
| Winrar | ✅ | ✅ | ✅ | ||
| PeaZip | ❌ | ✅ | ✅ | ||
| NanaZip | ❌ | ✅ | ✅ |
| Tool | Temporary Directory Pattern |
|---|---|
| 7z | 7z<Unique 4 characters String><Random 5 characters string> |
| Windows Explorer | Temp<Number>_<ZIP_File_Name> |
| Winrar | 💠Exeutable Files : Rar$EXa<Process ID>.<Random Numbers string>.rartemp 💠Other Than Exeutable Files : Rar$DIa<Process ID>.<Random Numbers string>.rartemp |
| PeaZip | 💠Exeutable Files : .pstmp<Random 6 characters string> 💠Other Than Exeutable Files : .ptmp<Random 6 characters string> |
| NanaZip | 7z<Unique 4 characters String><Random 5 characters string> |
| Password In Memory ( Plain Text )\Tool | 7z | Windows Explorer | Winrar | PeaZip | NanaZip |
|---|---|---|---|---|---|
| UTF8 | ❌ | ✅ | ❌ | ✅ | ❌ |
| UTF16-LE | ✅ | ✅ | ✅ | ✅ | ✅ |
7z Tool #
7z Website Link | Github Link
7z Tool is the most popular tool, it not only supports opening or creating archives of different formats, but it also helps to calculate the hash of files and support multiple type of compressions and archive types.
7z tool uses a simple approach when it creates temporary directories. The pattern the 7z tool uses for the temporary location is 7z<Unique 4 character String><Random 5 character string>. Example 7zO451CF4EE and the temporary directory is only created when the user opens a file from a zip archive.
If the user opens multiple files like blue.txt and yellow.txt from the same zip file, then there will be two different directory example, 7zO451CF4EE and 7zO451DA3AE. There is an observation in both names that the unique 4 character string is the same in both names O451. The 4 character string will only be same for all the files open during same 7z process/session, by this it means that if same archive is open multiple times then each time each process will have their unique 4 character string, This unique 4 character String can help analysts to find if user opened all the files from same 7z process or user opened the zip multiple times to access files from zip file.
If a zip file contains an executable file and the user executes the file from the zip ( Yes this is possible ), 7z will follow the same approach create a temporary 7z directory, and if the executable is launched from the same 7z process/session, then analysts will find the temporary 7z directory with the same unique 4 character string as other files. The only point to keep in mind is that the temporary directory will only contain the executable file, no additional files.
The important point to remember is that the 7z tool deletes the temporary directory instantly once the user terminates the process that opens the file or the executable process is terminated, but the 7z process should be present. If the 7z process is already terminated, then temporary files will be permanently present in the Temp Directory location, only system cleanup or the user can then delete them, 7z will never delete them.
Example:
# Zip File Directory Structure

                Colour
                  |
        ----------------------------------------------------------------
       |                                                 |             |
      red                                               blue.exe     blue.txt
      |
     ------------------------------------------------
    |               |                  |             |
   red.exe        red_require.dll    yellow.txt     green.zip
# User accessed blue.txt file
%AppData%\Local\Temp
|
7zO451CF4EE
|
blue.txt
# User also executed red file

          %AppData%\Local\Temp
                  |
          -----------------
          |               |
        7zO451CF4EE    7zO451DA3AE
          |               |
        blue.txt        red.exe
To understand how 7z deletes temporary files, let’s understand using 2 scenarios:
- Scenario 1: User close the zip file, and the 7z process is terminated, but the blue.txt file process is still not terminated, and the red.exe process is not terminated.
- Scenario 2: User terminated the blue.txt file process and terminated the red.exe process, and then closed the zip file, and the 7z process is terminated
In Scenario 1, both 7zO451CF4EE and 7zO451DA3AE temporary directories will not be deleted by 7z. In Scenario 2, both 7zO451CF4EE and 7zO451DA3AE will be deleted by the 7z tool and can’t be retrieved.
For the 7z tool, it is repeatedly mentioned in this research that file process not file, the reason is if user have text editor like sublime text, vscode or Windows 11 Notepad, these processes don’t terminate when the user closes the file, and therefore, even file is closed, because the process is not terminated, the 7z tool will not consider the file as closed.
Summary: #
- Temp Folder Name Pattern :
7z<Unique 4 character String><Random 5 character string> - The 7z tool stores opened files in the 7z temp folder, and each folder only has one file
- If multiple files are opened from the same 7z process/session, then the unique 4 character string will be the same for all temporary folders
- The 7z temporary directory will be deleted instantly once the file process is closed, and if the zip file is still open and the 7z process is not terminated
- The 7z temporary directory doesn’t get deleted if the file process is not terminated, but the zip file is closed, and the 7z process is terminated
WinRAR Tool #
WinRAR Website Link
WinRAR tool uses two file name pattern, Rar$EXa<Process ID>.<Random Number string>.rartemp when any executable is executed from a zip file and Rar$DIa<Process ID>.<Random Number string>.rartemp when any file other than an executable is opened from a zip file. The temporary directory name also provides the Process ID, which can help analysts to find the process in EDR or sysmon logs.
If multiple files are opened using the WinRAR tool from a zip file using the same process/session, then multiple directories will be created, and Rar$DIa<Process ID> will be the common, last Random Number string will be different. If any executable will be launched from the zip file, then the temporary directory name will be Rar$EXa<Process ID> but the process ID can help to identify that the activity was done from the same WinRAR process/session.
Before understanding how WinRAR deletes the temporary directories, let’s understand what files will be present in Rar$EXa<PID>.<Random Number string>.rartemp and Rar$DIa<PID>.<Random Number string>.rartemp directory.
Rar$EXa<PID>.<Random Number string>.rartemp: This directory is created because when an executable is launched from a zip file directly, this directory will contain all the files present in the zip file.
Example:
# Zip File Directory Structure

                Colour
                  |
        ------------------------
       |          |             |
      red        blue.exe     blue.txt
       |
     ------------------------------------------------
    |               |                  |             |
   red.exe        red_require.dll    yellow.txt     green.zip
# User accessed blue.txt file
%AppData%\Local\Temp
|
Rar$DIa6960.49245.rartemp
|
blue.txt
# User also executed red.exe file

          %AppData%\Local\Temp
                  |
          -----------------------------------------------------
         |                                                     |
Rar$DIa6960.49245.rartemp                             Rar$EXa6960.137.rartemp
          |                                                    |
        blue.txt                                              Colour
                                                                |
        ----------------------------------------------------------------
       |                                                 |             |
      red                                               blue.exe     blue.txt
       |
     ------------------------------------------------
    |               |                  |             |
   red.exe        red_require.dll    yellow.txt     green.zip
When an executable is executed, the temporary directory will be helpful for the analyst to find what files are present in the zip file.
The possible reason is executable dependencies. In the above example, red.exe has red_require.dll as a dependency, and if WinRAR only loads red.exe, then the red.exe process will not run properly because it needs red_require.dll.
Because 7z Tool only loads the executable in a temporary location, if any executable has any dependencies, then 7z Tool will not be able to run the executable.
Rar$DIa<PID>.<Random Number string>.rartemp: This temporary directory will only contain the file opened from the zip file, no additional files.
WinRAR tool behavior is unique and complex when it deletes the temporary files and directories.
-
The Rar$EXa<ProcessID>.<Random Number string>.rartemp- If executable is executed from a directory in that case all files in that executable directory will not be deleted even if executable process is terminated and WinRAR process is terminated.
- If executable is not executed from a directory in that only executable file will not be deleted if executable process is not terminated and WinRAR process is terminated. If executable process is already terminated then complete temporary directory get deleted by the WinRAR tool.
The temporary directory that is not deleted will be available on the system, and when next time user open the WinRAR tool, then WinRAR will check if there are any directories in the Temp Location that are older than one hour and then WinRAR will delete those directories.
-
The Rar$DIa<ProcessID>.<Random Number string>.rartemptemporary directory gets deleted when the WinRAR process is terminated. If the WinRAR process is already terminated, then the temporary directory will be available on the system, but files in the temporary directory will be deleted, and when next time user open the WinRAR tool, then the WinRAR tool will check if there are any directories in Temp Location and then delete those directories. Even if the temporary directory is not deleted, WinRAR will delete the file inside the temporary directory even if a file is still open. The WinRAR tool doesn’t delete files from the temporary location instantly when the file is closed, but the file will be deleted when the WinRAR process is terminated.
Example:
# User opened blue.txt and also executed the red.exe file

          %AppData%\Local\Temp
                  |
          -----------------------------------------------------
         |                                                     |
Rar$DIa6960.49245.rartemp                             Rar$EXa6960.137.rartemp
          |                                                    |
        blue.txt                                              Colour
                                                                |
        ----------------------------------------------------------------
       |                                                 |             |
      red                                               blue.exe     blue.txt
       |
     ------------------------------------------------
    |               |                  |             |
   red.exe        red_require.dll    yellow.txt     green.zip
# User terminated the red.exe process, but the blue.txt file process is not terminated
# WinRAR process terminated
%AppData%\Local\Temp
|
-----------------------------------------------------
| |
Rar$DIa6960.49245.rartemp Rar$EXa6960.137.rartemp
|
Colour
|
----------------------------------------------------------------
| | |
red blue.exe blue.txt
|
------------------------------------------------
| | | |
red.exe red_require.dll yellow.txt green.zip# User terminated the red.exe process and blue.txt file process
# WinRAR process is terminated
%AppData%\Local\Temp
|
Rar$EXa6960.137.rartemp
|
Colour
|
----------------------------------------------------------------
| | |
red blue.exe blue.txt
|
------------------------------------------------
| | | |
red.exe red_require.dll yellow.txt green.zip# New Zip File Directory Structure
------------------------
| | |
red blue.exe blue.txt
|
------------------------------------------------
| | | |
red.exe red_require.dll yellow.txt green.zip# User not terminated the blue.exe process
# WinRAR process is terminated
%AppData%\Local\Temp
|
Rar$EXa6960.137.rartemp
|
blue.exeAdditional observation for the WinRAR tool.
User opened the WinRAR tool at 00:00 AM and then opened a file from the zip file using WinRAR, and the file is open in Sublime Text, and the Sublime Text process is created at 00:05 AM then the WinRAR tool will delete the file from the temporary directory Rar$DIa<ProcessID>.<Random Number string>.rartemp and will not be able to delete the temporary directory
User opened the WinRAR tool at 00:05 AM and then opened a file from a zip file using WinRAR, and the file is open in Sublime Text, and the Sublime Text process is already created at 00:00 AM. In this case, because the Sublime Text process was started before the WinRAR tool, therefore winrar will delete the file and the temporary directory
Summary: #
Rar$EXa<PID>.<Random Number string>.rartemp- Created when executable launched from zip fileRar$DIa<PID>.<Random Number string>.rartemp- Created when a file other than the executable is opened from a zip file- Delete EXa directories after one hour when the WinRAR process starts again
- Delete DIa directory instantly only once the WinRAR process is terminated if the file is already closed.
- EXa directories contain all the files present in the zip file
- DIa Directory only contains files other than executable
Windows Explorer #
This is not any special tool this is the same Windows Explorer which is available in all Windows operating systems. Windows Explorer by default allow to open .zip files, windows explorer don’t allow open 7z or other zip/archive format files.
Understanding Windows Explorer’s temporary directory is easy, windows explorer create temporary directory with the pattern Temp<Number>_<ZIP_File_Name>. If a user opens a zip Zip_Test.zip, then the temporary directory name will be Temp1_Zip_Test.zip. If the same zip is opened multiple times, then the other directory name will be Temp2_Zip_Test.zip.
There is a point to remember, if a user opens two Explorer processes and in both processes the user opens the same Zip_Test.zip file, then the temporary directories will be Temp1_Zip_Test.zip and Temp2_Zip_Test.zip.
There is a difference between multiple processes and multiple windows. When a user opens the explorer process, by default the user can open any number of files and folders, and even if the user selects the option open in new window that doesn’t open a new explorer.exe process, it only creates a new window of Windows Explorer.
If want to test this, open Windows Explorer and then open another Explorer window and then check the process using tools like Process Explorer from SysInternals, and there will be only one process of explorer.exe. Check How Multiple Explorer.exe can be launched, to understand how windows explorer multiple process can be created.
Example:
# Zip File Directory Structure: ZIP File Name is - Zip_Test.zip

                Colour
                  |
        ----------------------------------------------------------------
       |                                                 |             |
      red                                               blue.exe     blue.txt
      |
     ------------------------------------------------
    |               |                  |             |
   red.exe        red_require.dll    yellow.txt     green.zip
# User opens zip in explorer.exe window 1: and opens file yellow.txt
%AppData%\Local\Temp
|
Temp1_Zip_Test.zip
|
Colour
|
red
|
yellow.txt # User opens zip in explorer.exe process window 2: and executes blue.exe
%AppData%\Local\Temp
|
Temp1_Zip_Test.zip
|
Colour
|
--------------------------------------------------
| |
red blue.exe
|
yellow.txt # User opens zip in explorer.exe process 1: and opens file yellow.txt
%AppData%\Local\Temp
|
Temp1_Zip_Test.zip
|
Colour
|
red
|
yellow.txt # User opens zip in explorer.exe process 2: and executes blue.exe
%AppData%\Local\Temp
|
------------------------------------------
| |
Temp1_Zip_Test.zip Temp2_Zip_Test.zip
| |
Colour Colour
| |
red blue.exe
|
yellow.txt Unlike WinRAR, Windows Explorer doesn’t load all files to the temporary directory, it will only load those files that are opened from a ZIP file.
Windows Explorer doesn’t delete the files instantly as the user closes the file or terminates the executable process, files are only deleted when the user accesses any folder or location in Windows Explorer other than a ZIP file or if the user terminates the explorer.exe process. If files are open or the executable process is not terminated, but the Explorer process is terminated, or the user accesses any other location from the same Explorer process, then Windows Explorer will delete the file other than the executable from the temporary location, and the executables will persist in the temporary location and system cleanup, or the user can only delete them.
Summary: #
- Temp Folder Name Pattern:
Temp<Number>_<ZIP_File_Name> - If ZIP_File_Name is the same and no previous temporary directory is present, then Explorer will reuse the number, but if a temporary directory is already present, then
Temp<Number>will increment - The Explorer.exe process only loads files to the temporary location that are open from a zip file.
- Explorer deletes the files when the Windows Explorer location is changed to a different directory then zip location or explorer process is terminated.
Peazip Tool #
Peazip Website Link | Github Link
According to PeaZip GitHub, PeaZip is a free archive manager utility for BSD, Linux, macOS, and Windows, which offers a cross-platform Open Source alternative to proprietary software (WinZip, WinRar, etc.), also available as a portable package not requiring installation. Works with 200+ archive types and variants (7z, ace, arc, brotli, bz2, cab, gz, iso, pea, rar, tar, wim, zip, zipx, zpaq, zstandard…), handles spanned archives (001, r01, z01…).
PeaZip follows the same approach as WinRar Tool, PeaZip also creates two temporary .pstmp<Random 6 characters string> and .ptmp<Random 6 characters string> directories based on different scenarios.
PeaZip doesn’t create .pstmp<Random 6 character string> and .ptmp<Random 6 character string> in the C:\Users\<username>\AppData\Local\Temp location. Peazip tool first creates the peazip-temp directory in C:\Users\<username>\AppData\Local\Temp location, and then the peazip-temp directory will have .pstmp<Random 6 characters string> and .ptmp<Random 6 characters string> directories.
Peazip Temporary Directory Structure:
            %AppData%\Local\Temp
                  |
             peazip-temp
                  |
     ------------------------------------------------
    |               |                  |             |
.pstmp1D2C77 .pstmpA8E104 .ptmp16F80A .ptmp576DF5-
.pstmp<Random 6 characters string>- This directory is created when the user launches the executable from the zip file. Peazip will load all files and directories from the zip to the temporary location. The reason is possibly the same as WinRAR because executables can have dependencies. -
.ptmp<Random 6 characters string>- This directory is created when the user opens any file other than an executable, and this directory only contains the file opened, and it follows the same directory structure as the zip file.
Example:
# Zip File Directory Structure

                Colour
                  |
        ----------------------------------------------------------------
       |                                                 |             |
      red                                               blue.exe     blue.txt
      |
     ------------------------------------------------
    |               |                  |             |
   red.exe        red_require.dll    yellow.txt     green.zip
# User opens blue.txt
%AppData%\Local\Temp
|
peazip-temp
|
------------------------------------------------
| | | |
.pstmp1D2C77 .pstmpA8E104 .ptmp16F80A .ptmp576DF5
|
Colour
|
blue.txt# User also opens yellow.txt
%AppData%\Local\Temp
|
peazip-temp
|
------------------------------------------------
| | | |
.pstmp1D2C77 .pstmpA8E104 .ptmp16F80A .ptmp576DF5
|
Colour
|
-------------------------------------------------------
| |
red blue.txt
|
yellow.txt # user also executed blue.exe
%AppData%\Local\Temp
|
peazip-temp
|
--------------------------------------------------------------------------------------
| | | |
.pstmp1D2C77 .pstmpA8E104 .ptmp16F80A .ptmp576DF5
| |
Colour --------------
| | |
---------------------------------------------------------------- red blue.txt
| | | |
red blue.exe blue.txt yellow.txt
|
------------------------------------------------
| | | |
red.exe red_require.dll yellow.txt green.zipEvery tool has something interesting and unique when it deletes temporary directories. PeaZip also has a unique way, if a file or executable process is terminated, then the PeaZip tool will delete the temporary directory only when the PeaZip process is terminated or the zip file is closed, But if file other than executable is open and then user terminate the peazip process then peazip will delete the temporary directory i.e, .ptmp<Random 6 character string>.
If the user executes a file from a zip file and then closes the zip without terminating the executable process, then in that case, Peazip will not be able to delete the directory completely, but it will delete the files from the .pstmp<Random 6 character string> directory which are not used by the executable process.
Example:
# Zip File Directory Structure

                Colour
                  |
        ----------------------------------------------------------------
       |                                                 |             |
      red                                               blue.exe     blue.txt
      |
     ------------------------------------------------
    |               |                  |             |
   red.exe        red_require.dll    yellow.txt     green.zip
# user executed red.exe
%AppData%\Local\Temp
|
peazip-temp
|
------------------------------------------------
| | | |
.pstmp1D2C77 .pstmpA8E104 .ptmp16F80A .ptmp576DF5
|
Colour
|
----------------------------------------------------------------
| | |
red blue.exe blue.txt
|
------------------------------------------------
| | | |
red.exe red_require.dll yellow.txt green.zip# user terminate peazip process without terminating red.exe
%AppData%\Local\Temp
|
peazip-temp
|
------------------------------------------------
| | | |
.pstmp1D2C77 .pstmpA8E104 .ptmp16F80A .ptmp576DF5
|
Colour
|
red
|
-----------------
| |
red.exe red_require.dll There is one more observation recorded for the peazip during this research, when user open any zip using peazip tool other than .pstmp<Random 6 character string> and .ptmp<Random 6 character string> there is one more directory created i.e, .pztmp in peazip-temp directory, when user open any file or directory in zip file then another directory created in .pztmp i.e, .pdtmp<Random 6 character string> and this .pdtmp directory will have two more directories source and virtual but these source and virtual directory are found always empty.
Example:
# Zip File Directory Structure

                Colour
                  |
        ----------------------------------------------------------------
       |                                                 |             |
      red                                               blue.exe     blue.txt
      |
     ------------------------------------------------
    |               |                  |             |
   red.exe        red_require.dll    yellow.txt     green.zip
# User opens blue.txt
%AppData%\Local\Temp
|
peazip-temp
|
---------------------------------------------------------------------
| | | | |
.pstmp1D2C77 .pstmpA8E104 .ptmp16F80A .ptmp576DF5 .pztmp
| |
Colour -----------------------------
| | |
blue.txt .pdtmp9CB8BA .pdtmpA57561
| |
---------- ----------
| | | |
source virtual source virtual# User also opens yellow.txt
%AppData%\Local\Temp
|
peazip-temp
|
---------------------------------------------------------------------
| | | | |
.pstmp1D2C77 .pstmpA8E104 .ptmp16F80A .ptmp576DF5 .pztmp
| |
Colour -----------------------------------------------------------------------------------
| | | | |
------------------------------------------------------- .pdtmp9CB8BA .pdtmpA57561 .pdtmp0941FD .pdtmp0941FD
| | | | | |
red blue.txt ---------- ---------- ---------- ----------
| | | | | | | | |
yellow.txt source virtual source virtual source virtual source virtualThe question can be why there are four directories when only two files are open. The reason is .pztmp creates temporary directories when the user opens a directory. In the above example user first opens the Colour directory -> blue.txt -> red directory -> yellow.txt, therefore, four .pdtmp directories.
Summary: #
.pstmp<Random 6 characters string>: When a file other than an executable is opened from a zip file.ptmp<Random 6 characters string>: When an executable is executed from a zip file- PeaZip tool first creates peazip-temp directory in
C:\users\<username>AppData\Local\Templocation and peazip-temp directory contains other temporary directories - .pstmp directory is created when the executable is launched from a zip file
- .ptmp directory is created when files other than the executable are opened from a zip file
- .pstmp directory contains all files from the zip, but once the zip is closed, it will delete all files except those files that are open or used by the executable.
NanaZip Tool #
NanaZip Website Link | Github Link
According to NanaZip GitHub, NanaZip is an open source file archiver intended for the modern Windows experience, forked from the source code of well-known open source file archiver 7-Zip.
Nanazip follows the same temporary directory structure as the 7z tool, 7z<Unique 4 characters String><Random 5 characters string> and it has the same approach as the 7z Tool, it creates a new directory when a file is opened from a zip file. The difference between 7z and nanazip is that when a user executes a file from a zip file, 7z only loads the executable file in a temporary location, but nanazip loads all the files to the temporary location. This is the same behaviour as peazip, as peazip also loads all files to the temporary location, but when the peazip process is terminated, if the executable process is not terminated, then peazip will remove all the files that are not used by the executable process, nanzip doesn’t delete anything and keeps all files in the temporary location.
Example:
# Zip File Directory Structure

                Colour
                  |
        ----------------------------------------------------------------
       |                                                 |             |
      red                                               blue.exe     blue.txt
      |
     ------------------------------------------------
    |               |                  |             |
   red.exe        red_require.dll    yellow.txt     green.zip
# NanaZip - user executed red.exe
%AppData%\Local\Temp
|
7zO451CF4EE
|
----------------------------------------------------------------
| | |
red blue.exe blue.txt
|
------------------------------------------------
| | | |
red.exe red_require.dll yellow.txt green.zip# NanaZip - user terminates NanaZip process without terminating red.exe
%AppData%\Local\Temp
|
7zO451CF4EE
|
----------------------------------------------------------------
| | |
red blue.exe blue.txt
|
------------------------------------------------
| | | |
red.exe red_require.dll yellow.txt green.zipnanazip deletes the temporary directory instantly as the user terminates the file or executable process if the nanazip process is not terminated.
# NanaZip - user open blue.txt
            %AppData%\Local\Temp
                    |
                  7zO451CF4EE
                    |
                  blue.txt
# NanaZip - user executed red.exe
%AppData%\Local\Temp
|
---------------------------------------------------------------------------------------
| |
7zO451CF4EE 7zO451DA3AE
| |
---------------------------------------------------------------- blue.txt
| | |
red blue.exe blue.txt
|
------------------------------------------------
| | | |
red.exe red_require.dll yellow.txt green.zipSummary: #
- Temp Folder Name Pattern :
7z<Unique 4 characters String><Random 5 characters string> - It creates a temporary directory when any file is opened
- If an executable is executed, then nanzip will load all files and directories in the temporary location
- The
7z<Unique 4 characters String><Random 5 characters string>directory is deleted instantly once the file is closed if the zip file is still open - The
7z<Unique 4 characters String><Random 5 characters string>directory doesn’t get deleted if the file is open, but the zip file is closed
If the user terminates the executable process and then, within milliseconds, also terminates the 7z or NanaZip process, then 7z or NanaZip will not be able to delete the executable temporary directory.
Zip File On USB #
There is no change found even if the Zip files are on the USB, if user opens the files from USB then also all the patterns for zip tools are same.
Forensic Evidences #
All the above information helps to understand the behavior of each zip tool, but as an analyst, what forensic artifacts will be created that can prove that the zip file is open, and when the zip file creates any temporary directories or create files in temporary directories and executes executables from the zip, then what other forensic artifacts are created for these activities. In this section, let’s explore more about the forensic evidence.
USNJRNL #
The USN Journal (Update Sequence Number Journal), or Change Journal, is a feature of the Windows NT file system (NTFS) which maintains a record of changes made to the volume. [ Source Wikipedia]
Tool that can be used to parse the USNJRNL file : MFTECMD
Evidence Recorded in USNJRNL #
| Tool | Temporary Directory Name | Temporary File Name | |
|---|---|---|---|
| 7z | ✅ | ✅ | |
| Windows Explorer | ✅ | ✅ | |
| Winrar | ✅ | ✅ | |
| PeaZip | ✅ | ✅ | |
| NanaZip | ✅ | ✅ |
MFT #
According to Microsoft Document, MFT is The NTFS file system contains a file called the master file table, or MFT. There is at least one entry in the MFT for every file on an NTFS file system volume, including the MFT itself. All information about a file, including its size, time and date stamps, permissions, and data content, is stored either in MFT entries, or in space outside the MFT that is described by MFT entries.
MFT records a lot of information about file like:
- Entry Number of file
- Parent Entry Number
- Parent Path
- File Name
- File Accessed, Modified, Created Timestamps
- Is File Copied etc..
Evidence Recorded in MFT #
Microsoft MFT Document says that as files are added to an NTFS file system volume, more entries are added to the MFT and the MFT increases in size. When files are deleted from an NTFS file system volume, their MFT entries are marked as free and may be reused. However, disk space that has been allocated for these entries is not reallocated, and the size of the MFT does not decrease.
When a user terminates the zip process without closing files #
| Tool | Temporary Directory Name | Temporary File Name | |
|---|---|---|---|
| 7z | ✅ | ✅ | |
| Windows Explorer | ✅ | ✅ | |
| Winrar | ✅ | ⚠️ | |
| PeaZip | ✅ | ✅ | |
| NanaZip | ✅ | ✅ |
⚠️ : Partial Information
- For the WinRAR Tool, MFT doesn’t record the file name only the temporary directory for files other than executables.
- For Windows Explorer and PeaZip, MFT will record all information about temporary files and directories, but mark the directories that are deleted by explorer.exe and the PeaZip tool as deleted
When the user closes files and terminates the zip process #
In the case when the user closes files and then terminates the zip process, it is unpredictable sometime MFT record information and sometimes partial information, and sometimes no information for temporary directories and files, and it is also not confirmed that every time the same partial information will be recorded. But still, the table below can provide information about what possible information can be found, and the information found in MFT can also change based on when files and directories are accessed from the zip file and when MFT is collected for investigation. As discussed above, MFT will mark the deleted entries, and MFT can remove the deleted entries and replace them with new entries.
| Tool | Temporary Directory Name | Temporary File Name | Notes | |
|---|---|---|---|---|
| 7z | ✅ | ✅ | .\PathUnknown\Directory with ID <Parent Entry Number>-<Parent Sequence Number> |
|
| Windows Explorer | ❌ | ✅ | .\PathUnknown\Directory with ID <Parent Entry Number>-<Parent Sequence Number> |
|
| Winrar | ⚠️ | ❌ | temp<Process Id>.<5 Random Numbers>.rartemp |
|
| PeaZip | ✅ | ✅ | ||
| NanaZip | ✅ | ✅ |
⚠️ : Partial Information
winrar can record sometime but not always
In case of Windows Explorer, 7z or any tool, if the user closes the files and then terminates the zip process, i.e, explorer.exe or 7z.exe etc.., in that case zip tool already deleted the temporary directory, and therefore the MFT entry will record the directory name as .\PathUnknown\Directory with ID <Parent Entry Number>-<Parent Sequence Number>.

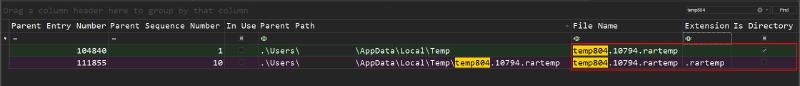
For the WinRAR tool, if the user closes all the files and processes and then terminates the zip process in that case WinRAR cleans the temporary location, and therefore MFT records the file name and directory as temp<Process Id>.<Random Numbers>.rartemp. The MFT was changed from Rar$DIa<Process Id>.<5 Digit>.rartemp to temp<Process Id>.<Random Numbers>.rartemp, but Process Id in directory name will depend on the process of winrar that deleted the winRAR file. For Example directory was created by process ID 1337 then directory name will have Rar$DIa1337.12345 but because file in temporary directory was not closed then process 1337 will not delete the file and directory but next time when WinRAR process starts, this time with process ID 1338 and process 1338 deletes the temporary directory and file, then deleted entry name will be temp1338.83467.rartemp, there is a issue with the filename, as filename will also follow same name as directory i.e, temp<Process Id>.<5 Random Numbers>.rartemp and no actual filename entry, the filename provided is incorrect information.
Prefecth #
The Prefetcher is a component of Microsoft Windows which was introduced in Windows XP. It is a component of the Session Manager Subsystem that can speed up the Windows boot process and shorten the amount of time it takes to start up programs. It accomplishes this by caching files that are needed by an application to RAM as the application is launched, thus consolidating disk reads and reducing disk seeks. [ Source Wikipedia]
As an analyst, thought can be ok, prefetch helps the operating system, but what is the importance of prefetch in Digital Forensics and Incident Response? The answer is the same as that help operating system and also helps analysts during investigation.
Prefetch records the following information:
- When the prefetch file was created ( i.e, when the first time executable was executed )
- Modify time, last access time
- Hash ( Hash of the complete path from where executable executed )
- Total Run Count
- Last 7 timestamps when the binary was executed
- Directories referenced
- Files referenced, etc..
Evidence Recorded in Prefetch #
As discussed above, the prefetch file is created when an executable is executed on the Windows operating system. Prefetch records a lot of information, like the timestamp when the executable was run for the last 7 times, total run count, and the most important information in this case is Files & Directories referenced.
Question can how Files & Directories referenced can be important during forensic investigation, especially during zip file investigations. Let’s understand each file.
Zip Tool Prefetch #
Zip Tool can provide information like which zip files are open by the zip tool, and you can correlate the last run time with the usnjrnl and MFT entries to find the zip file name and the files present in the file. This is observed that files & directories referenced will not always have zip file names.
Executable Launched From Zip Prefetch #
Is it possible to find the executable launched from which temporary location and from which zip tool? The answer is no, just by the name of the prefetch file, the analyst can’t find which zip tool started the executable process, and also it is not possible to find the location from where the executable is executed.
But when prefetch file information is parsed using tools like PECMD, then Files & Directories referenced will always contain from which location the executable is launched. There is again a problem when the executable is launched from 7z and Nanazip because both use the same temporary directory naming pattern, in this case, use the zip tool prefetch to find the last execution time and also check for the zip file name in Files & Directories referenced.
Text Editor Prefetch #
Text Editor can be used to read files, source code from zip files and because text editors like notepad, sublime Text etc.. also created their own prefetch files and they also record files and directories referenced and for any reason if USNJRNL and MFT records are cleared ( User can destroy USNJRNL & MFT ) then the prefetch can still provide some information about what are the file names and based on the file location as analyst it can be identified what zip tool was used and then prefetch file of zip tool can be checked to find the zip file name.
Can Actual Files or File Content Be Retrieved? #
By now, this can be clear that the answer is yes and no for the question if can actual files or file content be retrieved. As an analyst, the question can be if actual zip is already present on the user’s machine is then all the above investigation and evidence are important? The answer is yes because even if the zip file is present, how it can be proved the user opened the files from the zip file? To prove file access activity from the zip process will still require investigating USNJRNL, MFT, Prefetch & Temp Location.
Using MFT #
MFT, as discussed above store lot of information about files and in some cases MFT store the file content, Check Sans.org - NTFS: Attributes Part One blog.
Using Temporary Directory #
This completely depends on the analyst’s luck how the user closed the files and the zip tool. This is already discussed multiple times in this research that every time the analyst can’t get all the files from the temporary directory. The persistence of files in the temporary location depends on multiple factors does user closed the file before the zip tool, does zip tool cleans files on the next run, and how the zip tool handles executable files.
Bonus #
The question in corner of mind can be what will happen if the file contain large files like 3GB, 5GB in that scenario what will tools do? This section will answer this question.
Three points are checked when zip file have file that have file size greater than 4GB:
- Does Executable can execute the binaries as previously
- How temporary directories are deleted
- Is there any change observed for executables execution in case of large files
Executable files are specifically covered because zip Tools only create/copy all files to temporary directory in case of executables.
Tools like WinRAR and NanaZip are able to execute the binaries with dependencies and because both tool also copy/create all files from zip to temporary directory they also copy the large file and also a copy screen is shown. But Peazip tool is also able to execute the executable with dependecies and copy the large file to temporary directory but there will be no copy screen will be visible. 7z and Windows Explorer will not copy the large file to temporary directory as these tool don’t load files to the temporary directory.
| Tool | Can Run Executable | Does File Copy Window Visible | |||
|---|---|---|---|---|---|
| 7z | 💠With Dependencies: ❌ 💠Without Dependencies: ✅ 💠 Large File not copied to Temporary directory |
N/A | |||
| Windows Explorer | 💠With Dependencies ❌ 💠Without Dependencies: ✅ 💠 Large File not copied to Temporary directory |
N/A | |||
| Winrar | 💠 Executable Executed: ✅ 💠 Large File Copied To Rar$EXa directory |
✅ | |||
| PeaZip | 💠 Executable Executed: ✅ 💠 Large File Copied To .pstmp directory |
❌ | |||
| NanaZip | 💠 Executable Executed: ✅ 💠 Large File Copied To Temporary directory |
✅ |
Additional Resources #
Forensic Value of Prefetch - ICS SANS
Master File Table (Local File Systems) - Microsoft
Anatomy of an NTFS FILE Record - Windows File System Forensics - 13Cubed
WinRAR temporary folder artefacts - Geoffrey Fellows - Sciencedirect
Does WinRAR Leave Artifacts in Temp Folders that Show Changes to the Archive and Files? - WinRAR